1. A web address contains more than a domain name
When you type a web address into a browser, you provide a name that is convenient for people. Networks generally need an Internet Protocol, or IP, address to deliver traffic to a destination. The Domain Name System, known as DNS, connects these two worlds by looking up records associated with domain names.
Consider an address such as https://www.example.com/guides. The scheme, https, tells the browser which protocol to use. The hostname is www.example.com, while /guides identifies a resource on the website. DNS looks up the hostname; it does not search for the guides page or process the full web address.
DNS is often compared to a phone book, but it is better understood as a distributed database. No single server holds every domain’s information. Instead, different parts of the system direct queries toward the servers responsible for the requested name.
2. The lookup starts with information already nearby
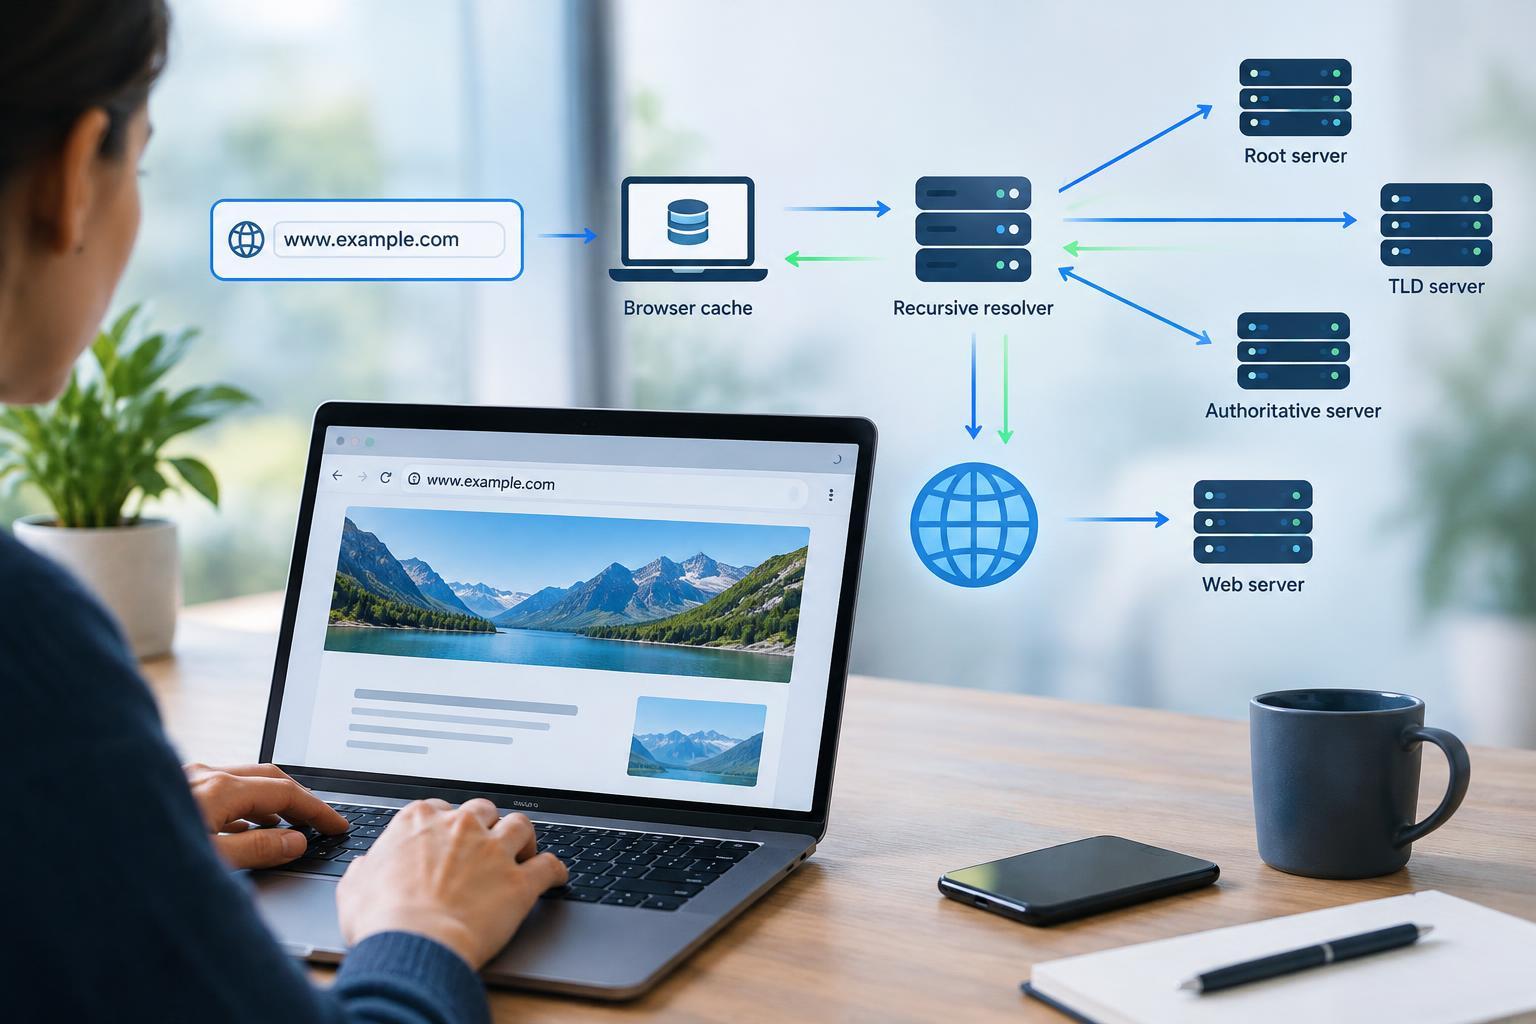
A browser may not need a fresh DNS lookup at all. It might already have a usable connection to the website or a cached DNS answer. Depending on the browser and device configuration, local caches and operating-system name resolution may supply the address before any external query is necessary.
If the answer is not available locally, the request usually goes to a recursive resolver. This service retrieves DNS answers on the client’s behalf. It may be operated by an internet provider, an organization or a public DNS provider. Some browsers use a separately configured resolver through encrypted DNS.
The resolver also maintains a cache, potentially serving many users. If it already has an unexpired answer for the requested name and record type, it can return that answer immediately. Caching is a major reason everyday browsing does not require a complete journey through the DNS hierarchy for every visit.
3. A resolver follows the DNS hierarchy
When the necessary information is missing from its cache, the resolver follows a chain of referrals. For www.example.com, it can begin by asking a root DNS server. The root does not normally provide the website’s IP address. Instead, it points the resolver toward the name servers responsible for the .com top-level domain.
A .com name server then supplies a referral toward the authoritative name servers for example.com. Those servers publish the DNS records for that domain’s zone. The resolver asks an authoritative server for the required record and receives an answer, an alias to follow or a response indicating that the requested information is absent.
This is the logical sequence, not necessarily a list of fresh network requests on every lookup. Cached referrals let resolvers skip steps they already know. The system also uses multiple servers and distributed infrastructure, so the root is not one machine through which all web traffic must pass.
4. DNS records provide addresses and other instructions
For a website connection, two important record types are A and AAAA. An A record contains an IPv4 address; an AAAA record contains an IPv6 address. A hostname can have multiple addresses, and a browser may evaluate available connection options rather than simply using one universal destination.
A CNAME record makes one name an alias of another. The resolver generally follows that alias to obtain the needed address records. DNS also supports other purposes: MX records identify mail servers, while TXT records carry text used for tasks such as domain verification and email authentication.
Records include a time to live, or TTL, which tells caches how long they may retain the information before refreshing it under normal operation. Changing a record therefore does not instantly replace every cached copy. Lower TTLs can shorten this delay, but they also tend to increase lookup traffic.
5. The browser connects, and HTTPS checks identity
After receiving a usable IP address, the browser can connect to that destination. For HTTPS, it establishes an encrypted connection using TLS, either over TCP or as part of QUIC for HTTP/3. Certificate validation helps confirm that the server is authorized to represent the requested hostname. DNS resolution alone does not establish that trust.
The destination may be a content delivery network, reverse proxy or load balancer rather than the machine that originally stores the website. DNS answers can vary according to service configuration, location or operational conditions. This allows one hostname to lead different users toward different infrastructure.
Once connected, the browser sends an HTTP request identifying the hostname and resource it wants. The server can then return the page. DNS helped locate an entry point; HTTP handles the request for content.
6. Understand what DNS can and cannot fix
A DNS failure can prevent a browser from finding a destination even when the website’s infrastructure is running. However, similar symptoms can come from a disconnected network, an unavailable server or a certificate problem. Flushing a local DNS cache may remove stale local information, but it cannot repair an incorrect authoritative record.
Security features address different risks. DNS over HTTPS and DNS over TLS encrypt queries between a client and its resolver, but the resolver can still see them. DNSSEC allows validating resolvers to check the authenticity of signed DNS data; it does not encrypt queries. Neither feature replaces HTTPS or guarantees that a website’s content is trustworthy.


