Three labels, different security boundaries
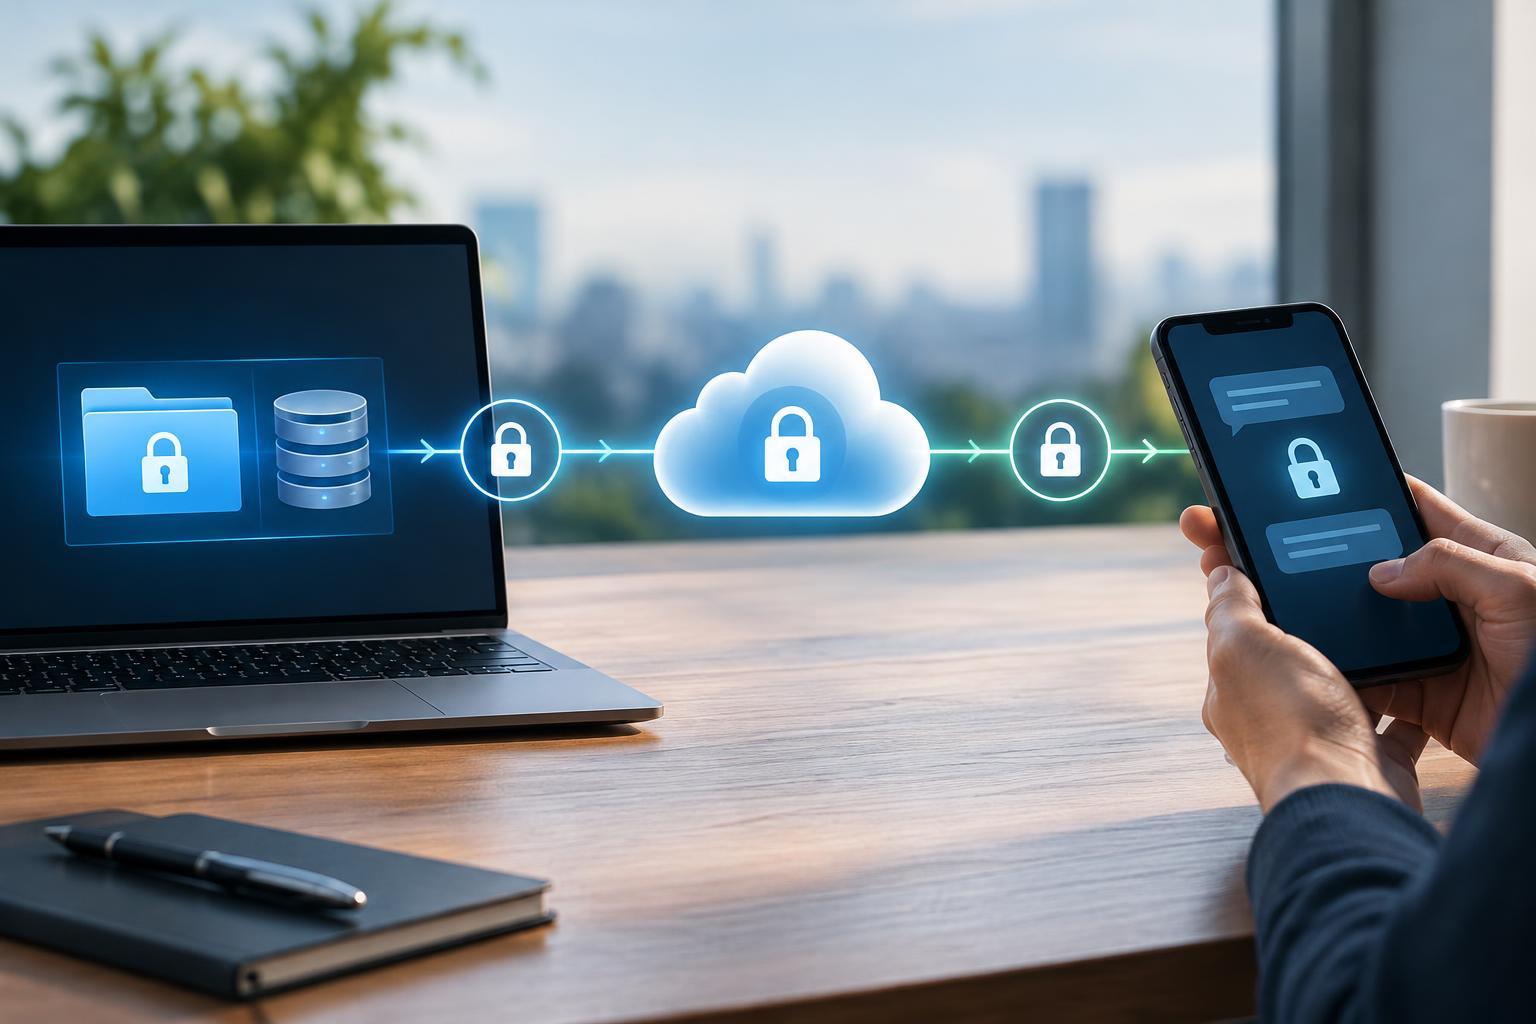
A file uploaded to a cloud service may be encrypted on your laptop, encrypted while traveling across the internet, and encrypted again on the provider’s storage. Yet the provider may still be able to read it. That is not necessarily a failure of encryption: each layer protects against a different kind of access.
Encryption at rest protects stored data. Encryption in transit protects data moving between specified endpoints. End-to-end encryption describes a boundary in which only the intended communicating endpoints hold the keys needed to decrypt the content. These protections can overlap. The useful question is not simply whether something is encrypted, but who can decrypt it, when, and on which devices.
Encryption at rest: protecting stored copies
Encryption at rest covers data stored on media such as laptop drives, server disks, databases, and backup devices. Full-disk encryption is particularly useful when a device is lost or its drive is removed, provided the relevant keys are not available to the person taking it. Database and application-level encryption can create narrower protection boundaries around selected records or files.
Its limits depend on where decryption happens. Once a computer is unlocked, applications running with sufficient permissions can generally access the files they need. Likewise, a cloud application may automatically decrypt stored records whenever an authorized user requests them. Storage encryption alone therefore does not stop an attacker who gains suitable application access, nor does it necessarily prevent the service operator from reading the data.
Key placement matters as much as the encrypted storage. Separate key management and carefully restricted permissions can improve protection, but they do not automatically make a system end-to-end encrypted. Temporary exports, logs, caches, and backups also need attention: protecting the main database does not establish that every copy is protected.
Encryption in transit: protecting the connection
Encryption in transit protects data as it moves across a network. HTTPS uses Transport Layer Security, or TLS, to protect the connection between a browser and the server that terminates that connection. With correct certificate validation and secure configuration, it helps prevent network observers from reading or altering the protected traffic.
The protection ends where that encrypted connection ends. A website server can normally read the request after decrypting it. If a content delivery network or reverse proxy terminates TLS, it can also access the traffic there; onward connections require their own protection. Multiple encrypted links can secure the route without hiding the content from the systems handling those links.
Transport encryption does not guarantee that a website is trustworthy or that its servers are secure. It also does not hide every network detail: observers may still see destination IP addresses, connection timing, and traffic volumes. A VPN similarly protects a particular network path; it is not, by itself, end-to-end content encryption between you and a message recipient.
End-to-end encryption: limiting who can read content
In an end-to-end encrypted messaging system, content is encrypted on the sender’s endpoint and decrypted on the intended recipients’ endpoints. The intermediary service carries encrypted content but is not given the keys needed to read it. This differs from ordinary HTTPS messaging, where a server can decrypt incoming messages and encrypt them again for delivery.
That stronger boundary still has edges. A compromised or unlocked endpoint can expose readable messages. A recipient can copy, screenshot, or forward content. Notifications, linked devices, and backups may introduce additional copies or access paths, depending on the product. End-to-end encryption also does not necessarily conceal metadata such as account identifiers, communication timing, or group membership.
The design must also establish whose keys are being used. Contact verification and device-change alerts can help users detect unexpected changes, where supported. The label alone does not explain how a system handles new devices, recovery, or key distribution; those details determine whether the intended boundary survives everyday use.
How to evaluate an encryption claim
Start with the threat you want to reduce. For a stolen laptop, full-disk encryption and a strong device lock are relevant. For interception on a network, correctly validated transport encryption matters. To keep message content unavailable to an intermediary provider, look for end-to-end encryption with clearly described endpoints and key ownership.
Then ask practical questions: Can the provider decrypt the content? Where does decryption occur? Are attachments, backups, and linked devices covered? What happens during account recovery? If server-side search, previews, or automated analysis are offered, ask how those features work without assuming that they either prove or disprove end-to-end protection.
Treat encryption as one layer rather than a complete security promise. Access controls, software updates, device security, retention settings, and recovery procedures remain important. A well-protected system combines appropriate encryption with controls for the moments when data must become readable.


