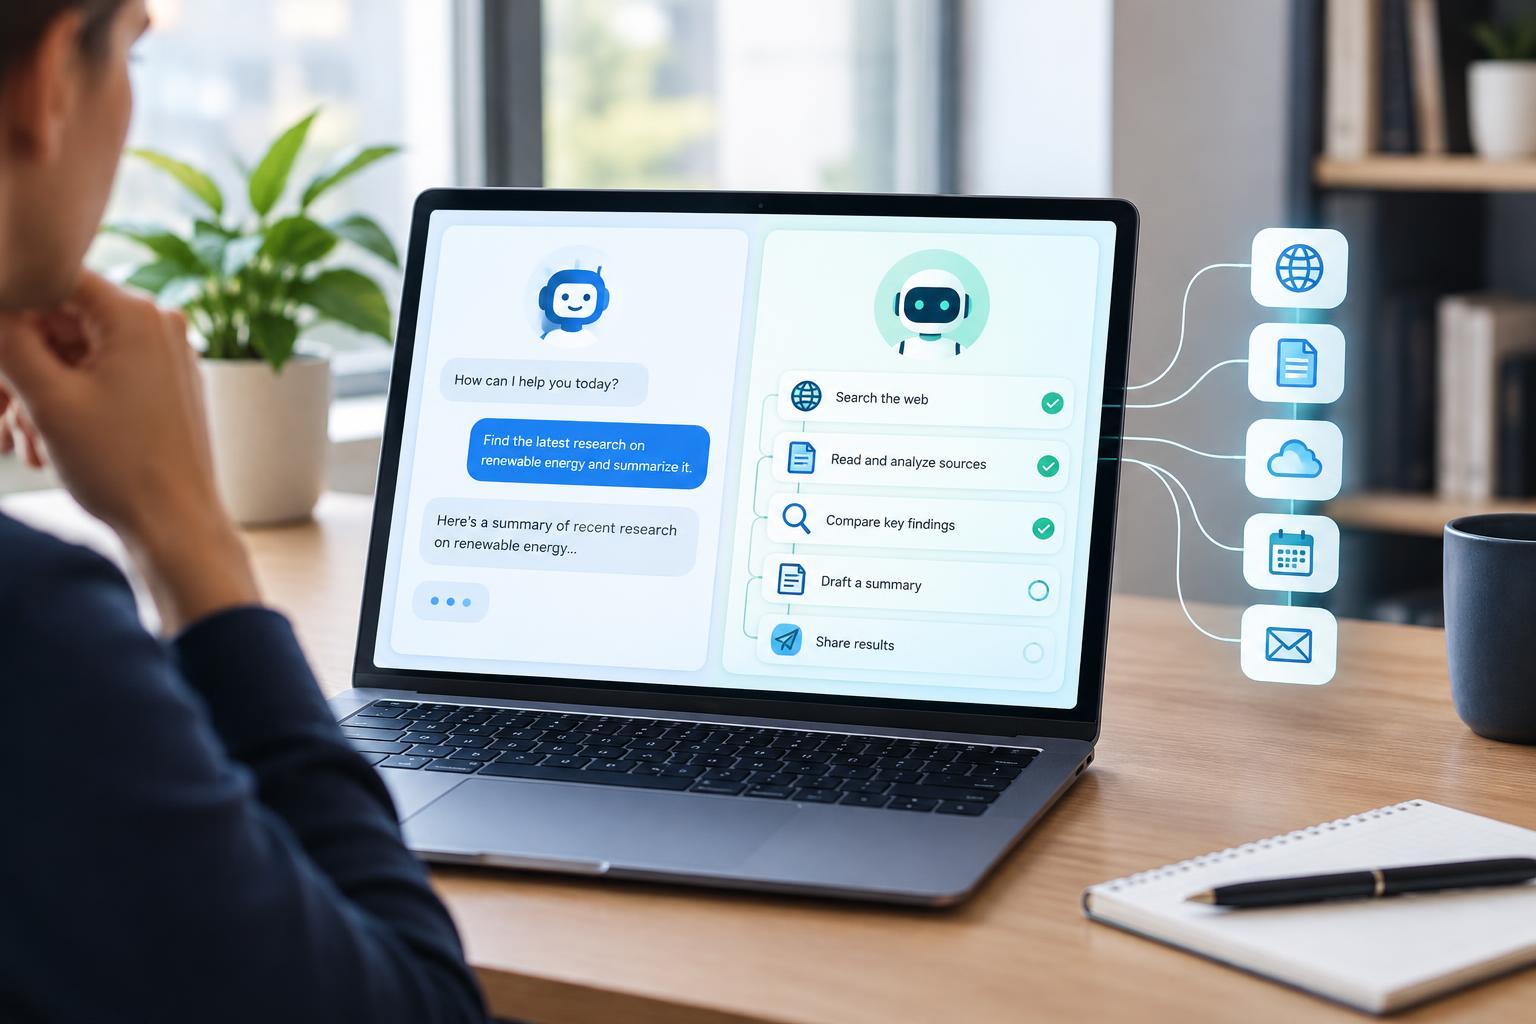
The Difference Is Behavior, Not the Chat Window
A chatbot is primarily designed to exchange messages with a user. It answers questions, explains information, or helps produce content. An AI agent is designed to pursue a goal by selecting and carrying out actions, often across multiple steps. Both may appear inside an identical chat interface, so appearance alone tells you little about what a system can actually do.
Consider a request to organize a meeting. A basic chatbot might suggest an agenda and draft an invitation. A tool-enabled chatbot might check calendar availability when asked. A more autonomous agent could compare schedules, propose a suitable slot, create an event, and notify participants, subject to its permissions and approval rules.
These labels are not standardized, and the boundary is not sharp. Some products called agents follow tightly prescribed workflows, while some chatbots perform substantial actions. The useful questions are operational: What can the system access? What can it change? Who chooses the next step? When must it stop and ask?
Tool Use Connects Language to Real Systems
Tools let an AI system interact with capabilities outside the language model. Examples include searching a document collection, running calculations, querying a database, retrieving order details, or sending a message. Rather than merely generating text about an action, the model can request an operation through a defined interface.
Tool use does not automatically make a system an agent. A chatbot that retrieves a delivery estimate through one predefined lookup is still operating within a narrow exchange. Likewise, a conventional workflow can execute several integrations without letting a model decide the sequence. Agentic behavior becomes more evident when the system chooses tools, interprets results, and adjusts subsequent actions toward a goal.
Reading and writing also carry different consequences. Looking up an inventory record is not equivalent to changing it. A sensible design separates read-only tools from tools that create external effects, validates tool inputs, and limits access to necessary resources. A model requesting an action should not, by itself, establish permission to perform it.
Autonomy Is a Set of Design Choices
Autonomy is better understood as a spectrum than a switch. At one end, the system suggests actions and waits for a person to execute them. Further along, it performs approved steps or runs a bounded workflow. At the higher end, it can choose intermediate tasks, react to changing conditions, and continue without approval for every individual action.
A common agent pattern is a repeated cycle: assess the task, choose an action, observe the result, and decide what comes next. This can be useful when the route to an outcome is not known in advance. However, it also creates opportunities for mistakes to compound. An incorrect assumption early in the process may influence several later decisions.
Useful autonomy therefore needs explicit boundaries. Set limits on runtime, tool calls, spending, and permitted destinations. Define what successful completion means and when the system should escalate uncertainty. Persistent memory is optional, not a defining requirement; when used, it needs clear rules about what is stored, who can access it, and when it expires.
Human Oversight Must Be Specific and Actionable
“Human in the loop” is meaningful only when the person has enough information and authority to intervene. An approval screen should explain the proposed action, its target, and important consequences. Asking someone to approve an opaque batch of operations can create the appearance of control without enabling careful review.
Match oversight to the stakes. Routine, reversible internal actions may be suitable for automatic execution within narrow limits. Publishing content, deleting records, changing access rights, or making commitments to customers may require explicit confirmation. Logs should record tool requests and outcomes so reviewers can reconstruct what happened. Where possible, provide cancellation and recovery mechanisms.
Systems that read emails, documents, or web pages must also account for malicious instructions embedded in that material. This is commonly called prompt injection. External content should be treated as data, not authority to override operating rules. Access controls and execution safeguards need enforcement outside the model, because instructions alone are not a dependable security boundary.
Choose the Smallest Useful Level of Agency
Start with the task rather than the label. If users mainly need explanations or drafts, a chatbot may be sufficient. If the process follows stable rules, a conventional workflow with limited AI assistance may be easier to test and maintain. An agent is worth considering when useful progress genuinely requires adapting the sequence of actions.
Pilot the system on a narrow, low-consequence task. Evaluate completed outcomes, incorrect actions, unnecessary tool use, escalation quality, and recovery from failures—not just how convincing its messages sound. Expand permissions only when the benefit justifies the additional exposure. The objective is not maximum autonomy, but dependable assistance with a clear boundary between what the system may decide and what remains a human responsibility.


